
Most enterprises already have AI governance problems before they have an AI governance program. Agents are answering customers, teams are spinning up MCP servers without central oversight, and token bills are arriving higher than anyone forecast. The instinct is to treat governance as the compliance layer that slows all of it down, but that framing has it backwards. The organizations moving AI from pilots into production can see what their agents are doing, predict what they'll cost, and shut them down when they misbehave. That visibility is what lets them scale.
Lisa Arthur is the Senior Vice President of North America & APAC at Sensedia, an API management and integration company whose platform includes an AI gateway for governing agents and model traffic. She's spent more than 30 years leading business strategy and go-to-market work at organizations including Akamai, Teradata, and Relativity, and is also the author of Big Data Marketing. In Arthur’s view, the debate over governance budgets starts from a flawed premise.
"AI governance isn’t a cost of scaling AI. It’s what makes scaling possible. Adoption without the architecture to make sure AI is doing the right things can become a costly governance nightmare," she says. Her view comes from conversations with CIOs and CTOs who are already running agents in production, often with less visibility than they assumed.
Governance moves out of the compliance column
Many of the leaders Arthur speaks with recognize the problem immediately, because they're already living with it. "They have ungoverned MCP servers, they have cost control issues with using different models, and they don’t know exactly what agents are giving to either their internal or external customers," she says. The risk of such an environment has already played out in public. Earlier this year, a user asked Chipotle’s customer service chatbot to write Python code before ordering lunch, and the bot complied.
Others, she says, still treat governance as something to minimize. "Some people think governance is a burden, because we think of it in old terms where governance equals compliance. That's really the wrong way to think about it," Arthur explains. She says budget conversations stall when governance is pitched in the abstract, and instead makes the case with three questions leadership should be able to answer on the spot. "If you can’t answer them and the board can’t answer them, there’s the business case."
The first question is what data each agent could expose to the employees or customers it serves. The second is whether the organization can forecast what its models will cost. "There’s this fear internally of a lot of people using AI, but once they do, token usage goes through the roof," Arthur notes. Her answer is to set spending thresholds and route traffic to a different model, including a self-hosted one, once a limit is reached.
The third question is how many MCP servers the organization runs and how many of them anyone actually controls. "That’s another area of concern we’re getting from CTOs and CIOs. They don’t know, because people can spin up an MCP pretty easily, and those are also points of risk," she says.
Two-week pilots built to reach production
For organizations without mature governance, Arthur says the starting point is getting out of the pilot phase. "We work with clients to do two-week proofs of concept, and those pilots are two weeks because they're scoped to end in production for one use case with success criteria fixed on day one, live and governed on day fourteen. Then repeat across use cases."
The pilot should center on the use case where governance matters most, and it should produce an outcome rather than a list of lessons learned. One international financial services firm she works with chose lending and credit scoring. The team mapped what the agent was doing and how to govern it, then took the use case live after two weeks. From there, the work repeats across use cases, connecting the organization’s MCP servers and agents into a single view.
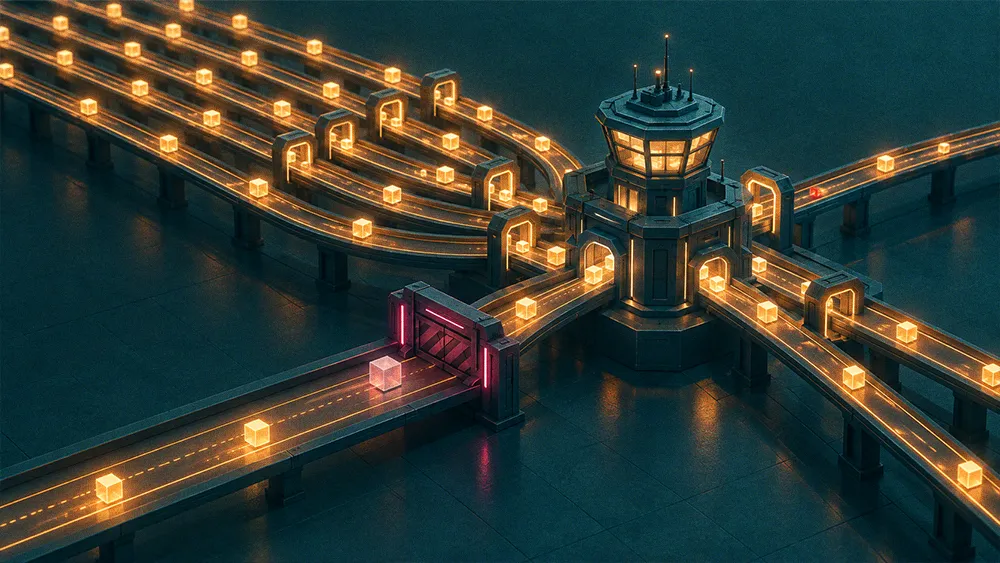
"It really comes down to a simple concept of an integrated, neutral backbone for AI that unifies the control plane. Think of it almost like a control tower that allows you to see, move, and give instructions," Arthur explains. The quick wins build the confidence to expand. "The problem isn’t AI adoption. It’s AI at operational scale."
Visibility into agents you don’t own
Third-party agents are where many leaders assume control ends, since a vendor may govern its own agent behind a wall the customer can’t see past. Arthur sees that boundary differently. "You may not see inside a vendor's agent, and you don't need to. The moment that agent's traffic crosses your edge—your APIs, your MCP servers, your models—that's your control point. With an independent gateway there, you can observe every call it makes, apply policy to each one, and revoke its access the moment something looks wrong," she says.
That reach extends to stopping an agent outright. "It's not about owning the agent. It's about owning the door it walks through," Arthur notes. "If the traffic crosses your gateway, you can see it, check it, and cut it off. That's control." Most organizations are far from it today. Research Sensedia conducted with MIT Sloan Management Review and Squadra found that 71% of tech professionals and 81% of tech executives operate with basic or no control over AI outputs.
Independence also matters when choosing the governance tooling itself. "Selecting a vendor-neutral solution to provide the guidance of any model, any agent, and any system is critical, because it prevents vendor lock-in," Arthur says. "Vendor lock-in is a death sentence in AI."
Familiar patterns, new stakes
Arthur wrote a book on big data, and she sees parts of that era repeating. "Enterprises hear a word and they think they need to go there. They maybe don’t fully define it within their company, they don’t have alignment on what it means, and then they start doing pilots and projects and they don’t get the results," she says.
The scope of exposure is what has changed. "What’s different is the ubiquity, the power, and the risk that AI introduces into the organization, big and small," Arthur explains. Treating agents like another application rollout is the mistake she sees most often. "If we approach it like we have every other technology, it’s never going to see the realization, and it’s going to bring a lot of headaches," she concludes.